Prove that a file existed — free, public, and verifiable without trusting us.
Your file never leaves your device: only its SHA-256 fingerprint is recorded, at the exact @beat. Anyone can check it later — without asking us.
No cookies · No trackers · No account · Free, open API · 11 languages
Every day
Proofs in Bitcoin blocks
Every week
Weeks anchored by a bank
Every quarter
Complete log with a DOI
BitcoinOpenTimestampsGitHubInternet ArchiveZenododrand
Tools in your browser
Nothing to install and no account. Your files stay on your device.
Timestamp
Drop any file: its fingerprint is stamped at the current @beat. You get a PDF certificate with a QR code and an offline proof file.
Timestamp a file — freeTime capsule
Seal a message or a file so that no single key holder can open it before a chosen @beat — not even us. Sealed in your browser.
Seal a capsuleCheck a file handover
Received a Sigelith Handover evidence package or a defect proof? Check the signatures, receipts and dates — nothing is uploaded.
Check a file handoverCheck any file
Not sure what you have? Drop a .beatproof, a certificate PDF, a package or any other file, and the right check starts by itself.
Check any fileOn your Windows computer
Sigelith Desktop timestamps files without uploading them, verifies proofs offline, watches the public log’s witnesses and hands over files with proof of delivery.
- Timestamp files
- Verify without trusting us
- Hand over files with proof of delivery


Sigelith Backup
Versioned backups to an external drive — and a safe place for your Sigelith proofs.
About Sigelith Backup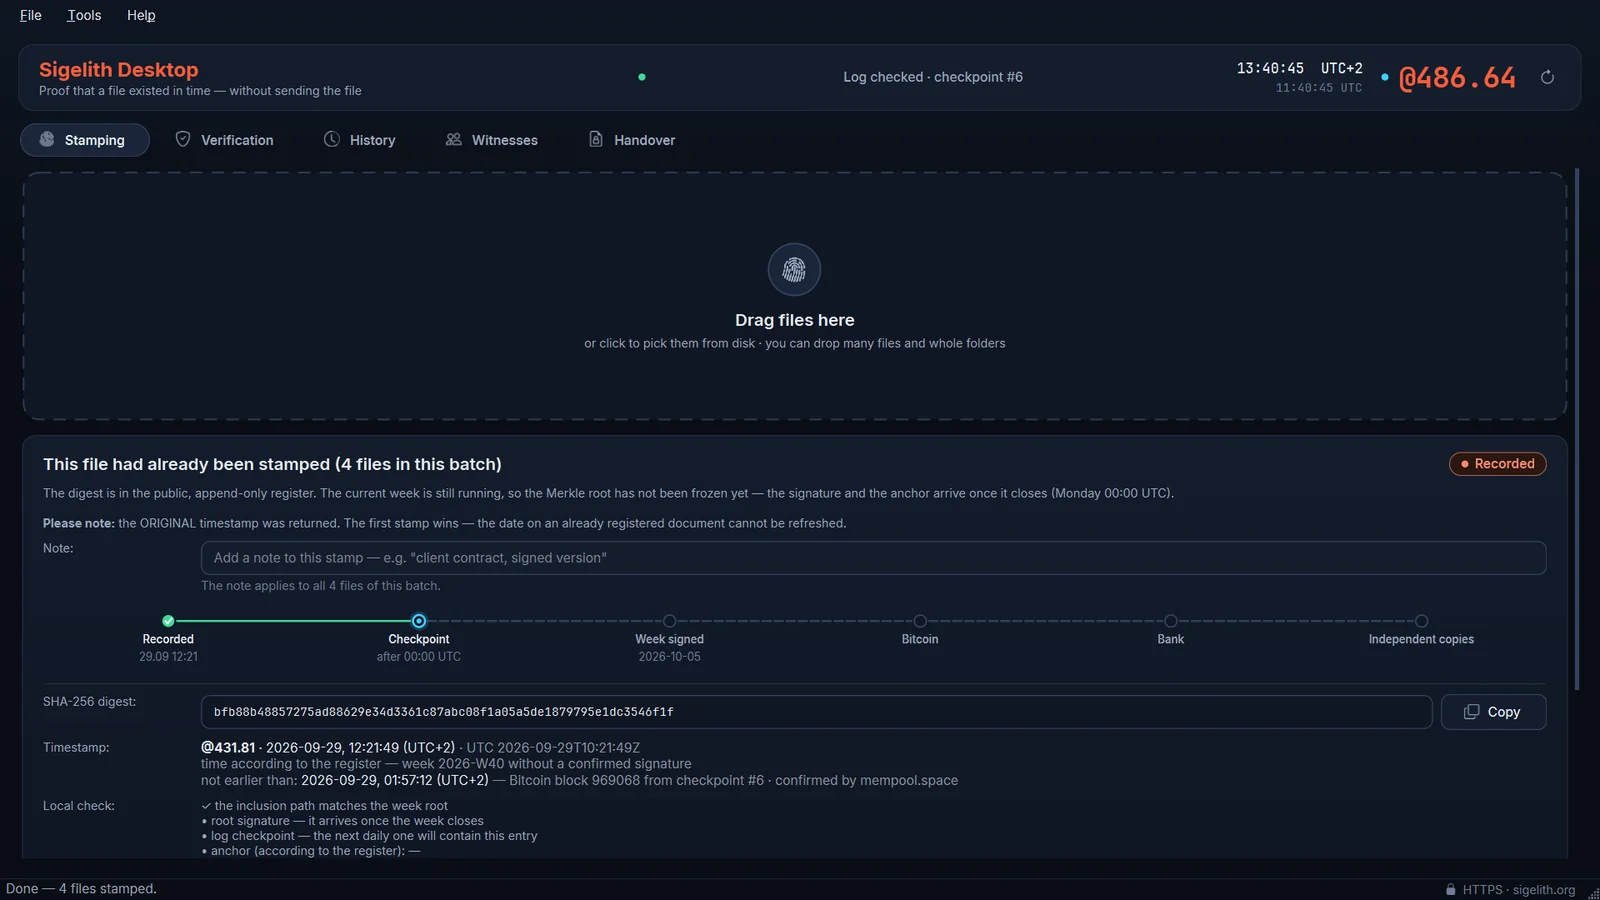
On your phone and wrist
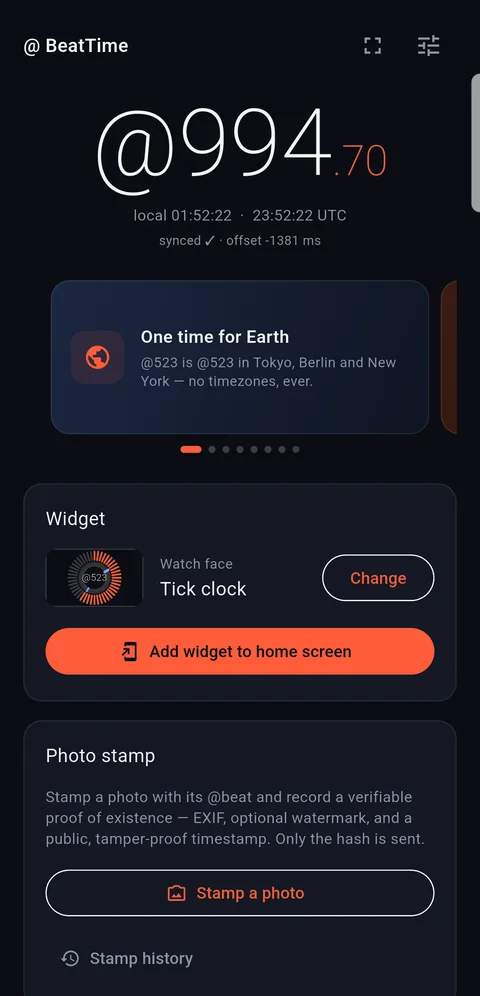
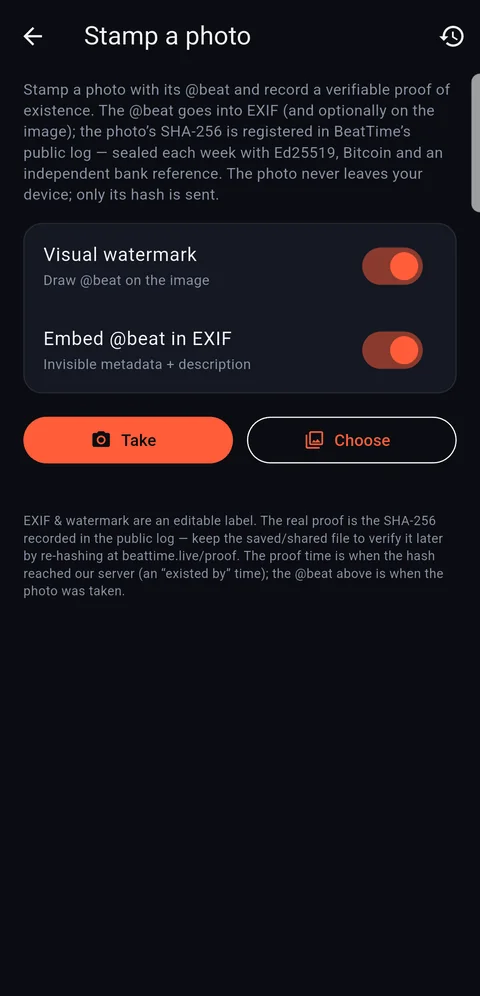
Free @beat clock for Android: 13 home-screen widget faces, a Wear OS watch face, a flip-phone cover clock, photo stamping and a converter. No ads, no tracking.
For developers
A free public API with no key and no account: stamp, verify and read the time from your own code. Every format is documented and every client is open source.
API reference
Every endpoint with a live console, generated from the OpenAPI schema.
Open the referenceWidget & SDKs
A live @beat clock on any website from one line of HTML, and clients for Python, PHP, JavaScript, C# and C++.
Embed the live clockSpecifications
The proof format, the capsule format and Handover — everything you need to verify without us.
How it works
Five steps from your file to a proof that anyone can check — without trusting us.
-
1
Fingerprint
Your browser computes the file’s SHA-256. The file itself never leaves your device.
-
2
Public log
The fingerprint enters an append-only log at the current @beat, chained to every entry before it.
-
3
Signed checkpoints
The log is sealed in signed checkpoints, so any attempt to rewrite its history — including by us — would be visible.
-
4
Bitcoin and a bank
Every day the log is committed to Bitcoin; every week its root is anchored in a bank transfer record.
-
5
Copies with third parties
Every week the log is copied to GitHub and the Internet Archive, every quarter to Zenodo with a DOI.
Nobody holds the key alone
A sealed capsule is locked by independent parties at once. The drand signature that unlocks it only comes into existence at the @beat you choose, and key servers release their shares only after it — so no single key holder can open it early, not even us.
drand · League of Entropy
A public threshold network run by independent organisations, including Cloudflare, Protocol Labs and EPFL. It signs a new round every 3 seconds; the signature that unlocks your capsule does not exist until your moment.
Sigelith Key · beat-key
Our own key server releases its share only after the moment has passed. It is open source (Apache-2.0), with reproducible builds and signed releases — anyone can rebuild it and compare.
An independent operator
A second key server run by Konveria in Kraków — an independent company with no personal or capital ties to us, which also publishes our Android apps on Google Play — on another hosting provider, in another country. Two shares never share an owner or a hosting provider.
Your recovery code
Stays with you. It stands in for one key holder if an operator ever disappears — on its own it never opens a capsule early.
Live right now: drand quicknetSigelithbeatkey-konveria
Seal a capsule Capsule format Operator registry beat-key source code
Verifiable without taking our word for it
Timestamp any file with @beat — free and public. Your file never leaves your device; only its SHA-256 is recorded. Later, prove the document existed at that moment.
Support Sigelith
Sigelith is free – no ads, no tracking, no account. If it is useful to you, you can leave a voluntary tip. Nothing is unlocked and nothing is held back.
FAQ
Does my file leave my device?
No. Your browser computes the file’s SHA-256 fingerprint and sends only that: 64 characters from which the file cannot be rebuilt.
Is the proof of existence really free?
Yes. Your file is hashed in your browser — only its SHA-256 reaches our server. Every day the whole log is signed and committed to Bitcoin; every week it is anchored in a bank record and copied to GitHub and the Internet Archive; every quarter to Zenodo. You get a PDF certificate with a QR code. Why it is free — read the manifesto.
Can I verify a proof without Sigelith?
Yes. A proof carries the path to a signed weekly root, and that root is anchored in Bitcoin and a bank record and copied to GitHub, the Internet Archive and Zenodo. The specification and the verifiers are open source. Proof spec
Can anyone open a sealed capsule early?
No single key holder can — not even us. In the standard profile any two of three parts open it: the drand network’s signature for that @beat, the share of our own key server and your recovery code. The drand signature only comes into existence at the @beat you choose; our key server releases its share only after it — by policy, not by cryptography. So whoever holds your recovery code needs only us to break that policy: keep the code apart from the capsule file.
What is Sigelith Handover?
A way to hand over files with proof of delivery. The recipient accepts with their own key, the moment of delivery is stamped in the public log, and both sides keep an evidence package that anyone can check on this site. The Sigelith server never sees the files. Check a file handover
Is there a free API?
Yes — a free, public REST API with no key and no account: timestamp a hash, verify a proof, read the public log and the current @beat. See the developer docs at sigelith.org/docs.
Which apps are there?
Sigelith Desktop for Windows (in the Microsoft Store), with Sigelith Backup as a companion for backups; BeatTime for Android with a separate Wear OS watch face; and two Android apps for parcels: Sigelith Courier for couriers (coming soon) and Sigelith Delivery for recipients (on Google Play), who can also confirm in any browser. All apps
What is the @beat in every timestamp?
Sigelith writes times in @beat: the day is split into 1000 beats of 86.4 seconds, anchored to UTC. @500 is noon UTC — the same moment everywhere on Earth. The @beat clock